A quiet but consequential shift is underway in how people protect themselves online. For over a decade, the standard advice was simple: pick a VPN provider with a strong "no-logs" policy and trust that promise to hold. That approach is losing credibility fast, and the reason is structural, not just reputational - a corporate pledge is only as durable as the legal jurisdiction that can override it.
The weakness becomes obvious the moment a government agency issues a subpoena. Centralized VPN providers, however well-intentioned, operate out of data centers with fixed addresses and corporate registries. When legal pressure arrives, the "no-logs" claim often turns out to be more marketing than architecture. This matters for everyday use cases too - plenty of people rely on these tools simply for things like watching BBC iPlayer while travelling, only to discover that centralized servers are easy for both regulators and content platforms to identify and block. The infrastructure itself, not just the policy on top of it, has become the point of failure. watching BBC iPlayer while travelling
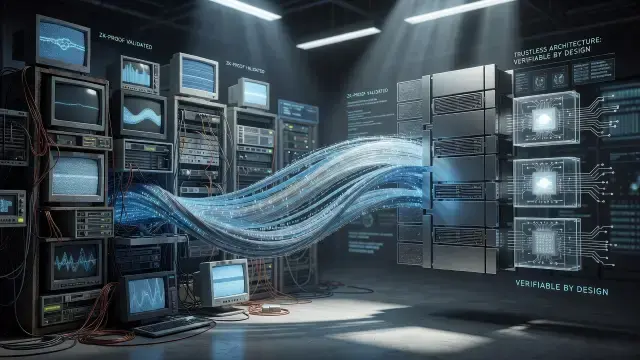
State-level censorship systems have grown sophisticated enough to recognize the IP ranges that commercial VPNs use. They flag them, throttle them, and eventually block them outright, forcing providers into an endless game of swapping server addresses. A decentralized VPN, or dVPN, sidesteps this by removing the central target altogether. Instead of one organization owning the servers, the network is built from thousands of independently operated nodes - ordinary people sharing spare residential bandwidth through a peer-to-peer marketplace. There is no single headquarters to subpoena and no uniform IP range to blacklist.
Why Residential Infrastructure Changes the Threat Model
The distinction between a data-center IP and a residential IP is not a technicality - it is the core of why dVPNs resist censorship more effectively. Firewalls are built to recognize data-center traffic because that is where commercial VPNs have always lived. When your connection instead routes through someone's home internet, you look like any other resident browsing the web. This is the underlying logic of Decentralized Physical Infrastructure Networks, or DePIN: ownership and operation are distributed across users rather than concentrated in a corporation, which removes the predictable choke points that censors exploit.
This does not mean every network marketed as "decentralized" delivers on that promise. Some operate thousands of nodes that are, in practice, clustered inside the same handful of cloud providers - offering no real resistance to blocking. Genuine decentralization requires geographic spread, residential ISP diversity, open-source and audited protocols, and a tokenized, pay-as-you-go cost structure that rewards node operators for reliability rather than locking users into subscriptions.
What Responsible Use Still Requires
None of this removes the need for judgment. Laws on circumventing firewalls differ sharply between countries, and users should understand local rules before relying on any privacy tool. Usability also still matters: a dVPN that demands fluency in crypto wallets and smart contracts will fail most people in the moments when they need it most. The platforms gaining real traction are the ones that hide that complexity, offering one-click connections while keeping the cryptographic guarantees running underneath. Privacy, in other words, is becoming less about promises and more about design - systems built so that trust is no longer the thing being asked for.